Regulators and underwriters don't have to prove negligence — an empty file does it for them. See what the law expects →
See the actual artifacts.
Before you generate your own.
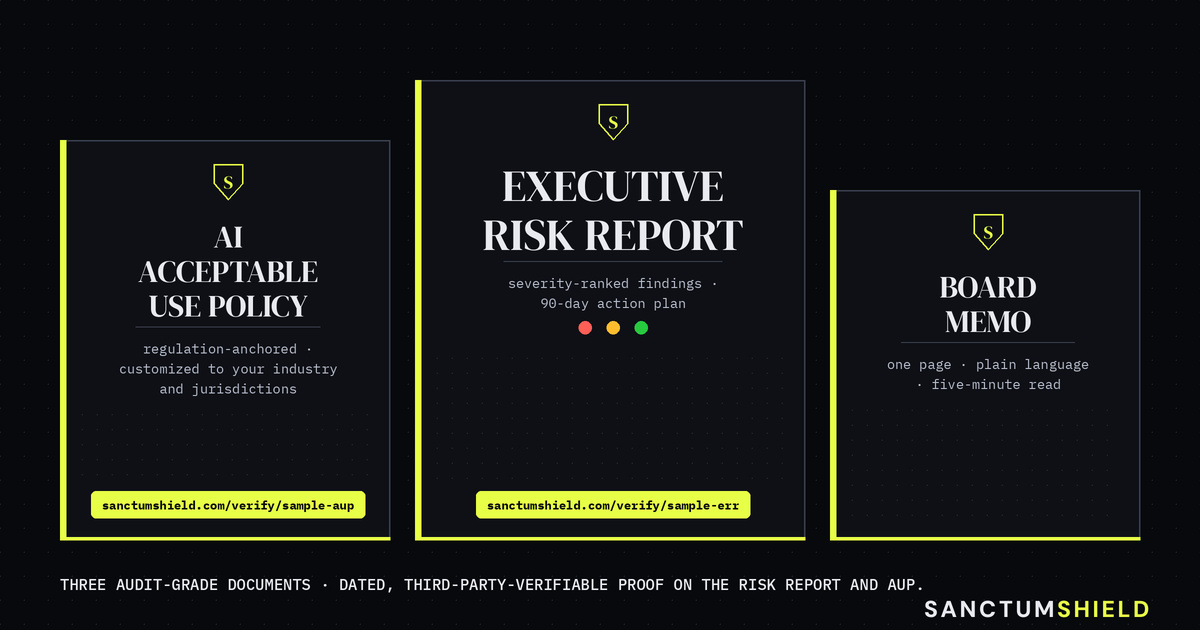
These documents sit alongside a compliance program such as Vanta: board-voice narrative documents, portable verification URLs, and a 90-day remediation plan in the customer's hand. See how SanctumShield works alongside Vanta.
Three rendered SanctumShield deliverables for a fictional 240-employee healthcare SaaS named Acme Health — the same Acme Health referenced on the Explainer and How It Works pages. Every value is fictional. No real PHI, no real findings against any real organization.
6 findings · findings that compound · impact-first severity rationale.
Sample shows: 5 regulation-anchored findings ordered by severity (CRITICAL → MEDIUM), one “Findings that compound” callout, per-finding confidence rating, severity rationale (impact-first model), policy coverage count, and a 90-day action plan.
Executive Shadow AI Risk Audit
Acme Health, Inc.
Due diligence: on April 26, 2026, Acme Health, Inc. identified the AI it uses and considered these AI governance questions, recorded here with its answers. Due care: each open item has a named owner and a next step, and the next review records what was completed. This record is evidence of that process. It is not legal advice or a statement of compliance.
Scope: Complete review, selected by Acme Health, Inc.. All twelve areas of AI governance considered.
At a glance
- What AI you have: 5 AI tools and built-in AI features and 3 agents are on record.
- What you decided: Leadership has recorded a decision on 2 of 11 findings (1 to fix, 1 accepted); 9 have no decision yet.
- Who owns it: One named person is accountable for AI governance: Chief Compliance Officer. No agent has a named person who can stop it yet.
- What is recorded: written AI policy: No; role-based training: Some people or general training only.
- Overall risk: HIGH tier, 11 findings, 7 rated high or critical. Each finding lists an owner and a next step.
What changed since last time
No earlier assessment came with this run, so this report is the first on record for comparison. Your next report will list what changed since this one.
Executive Summary
Acme Health operates in a regulated healthcare environment with substantial AI exposure across all three layers of the SanctumShield assessment model. The most material risk is unmanaged Microsoft 365 Copilot usage on a tenant containing Protected Health Information (PHI), with no AUP coverage and no business associate agreement specific to the Copilot service. Without immediate remediation, Acme Health is one configuration change away from a HIPAA notification trigger.
Four additional findings — unmanaged Cursor agent usage on engineering laptops, no formal AI Acceptable Use Policy, no published sub-processor disclosures, and an unrestricted BYOD posture invisible to MDM — compound the posture into a TOXIC_COMBINATION. Recommended remediation begins within seven days; full closure is achievable inside 90 days under the action plan in this report.
Findings that compound
These findings reinforce one another. Addressing them together, with one owner, closes more risk than addressing each on its own.
Untracked Copilot exposure on PHI tenant
Findings F1 + F3 + F4 combine into an aggregate posture where PHI flows through an AI surface with no policy, no sub-processor disclosure, and no executive review cycle. Each finding is individually addressable; together they constitute an exploitable governance exposure.
Key Findings
Microsoft 365 Copilot uncovered on PHI tenant
Copilot is enabled on the Acme tenant and reads SharePoint, OneDrive, and Exchange data including PHI. The current AUP does not address Copilot, and no BAA addendum has been executed with Microsoft for the Copilot service specifically.
Unmanaged Cursor agent usage on engineering laptops
Engineering team uses Cursor with autonomous-agent features enabled. No AUP coverage, no review cadence, no documented allowlist of MCP servers Cursor agents are permitted to invoke.
No formal AI Acceptable Use Policy in place
Acme has no published AI Acceptable Use Policy covering AI tools, agents, or embedded-AI features. The policy gap blocks SOC 2 attestation for AI-specific controls and creates a documented exception under EU AI Act Article 14 for any high-risk processing.
No sub-processor disclosure for AI vendors
Acme has not maintained a sub-processor list documenting which AI vendors process customer data on the platform's behalf. GDPR Article 28 requires data controllers (Acme's customers) to be notified of new sub-processors with the right to object.
BYOD AI posture invisible to MDM, EDR, and DLP simultaneously
Personal devices are allowed unrestricted access to corporate Google Workspace and M365 via OAuth. The AUP does not prohibit personal-device AI tools (Cursor, Ollama, Claude Desktop, n8n) on corporate data. This is a Layer 3 blind spot the existing security stack cannot see.
Retrieval Provenance Gap
Microsoft 365 Copilot answers from Acme Health's payer-policy documents to draft prior-authorization letters, and those answers are not required to carry the document, version and page or section they relied on. An answer drawn from a company document is evidence only if it can be traced to a location in that document.
Tool Risks
| Tool | Risk | Recommendation | Why |
|---|---|---|---|
| Microsoft 365 Copilot (Layer 2 · embedded) | CRITICAL | Approve with conditions | Reads PHI tenant data with no AUP coverage and no Copilot-specific BAA addendum. |
| Cursor (Layer 1 · direct) | HIGH | Approve with conditions | Autonomous-agent features enabled on engineering source code containing customer identifiers. |
| Google Workspace Gemini (Layer 2 · embedded) | HIGH | Approve with conditions | Same scope as Copilot; AUP also does not cover. |
| ChatGPT (Layer 1 · direct) | MEDIUM | Approve with conditions | 443 connections in the trailing 30 days; consumer-tier accounts cannot be confirmed. |
| Notion AI (Layer 2 · embedded) | MEDIUM | Approve | Knowledge-base search agent on workspace containing customer data. |
Regulatory Exposure
Acme Health's declared scope (HIPAA + SOC 2 + GDPR) is materially exposed by the combination of unmanaged Copilot on a PHI tenant and the absence of an AI AUP. Under HIPAA §164.502(e) the lack of a Copilot-specific BAA exposes Acme to penalty risk if PHI flows through the service. Under SOC 2 CC5.3 the AUP gap is a documented exception that the 2026-Q3 Type II audit will flag. Under GDPR Article 28 the missing sub-processor disclosure triggers the right to object for any EU-resident customer. Address within 30 days to avoid a HIPAA notification cascade and a SOC 2 audit exception.
90-Day Action Plan
-
Week 1 — Disable Copilot tenant-wide pending policy adoption and Microsoft Copilot-specific BAA execution. Closes F1 and TC1.
Owner: CISO · Effort: LOW · Confidence: HIGH -
Week 2 — Adopt SanctumShield-generated AI Acceptable Use Policy (16 sections, regulation-anchored) and route for CISO + GC + CEO signature. Closes F3.
Owner: Legal · Effort: MEDIUM · Confidence: HIGH -
Week 4 — Publish AI sub-processor disclosure on the trust page and notify enterprise customers with a 30-day right-to-object notice. Closes F4.
Owner: Legal · Effort: MEDIUM · Confidence: MEDIUM -
Week 6 — Implement managed-device conditional access for corporate OAuth across Google Workspace and M365. Closes F5.
Owner: IT · Effort: HIGH · Confidence: MEDIUM -
Week 8 — Roll out company-wide AI safe-use training with mandatory acknowledgment tied to the new AUP. Closes F3.
Owner: HR · Effort: MEDIUM · Confidence: HIGH
Coverage check: 5 of 7 findings and combinations are closed by an action. Not closed by an action, with its owner:
- F2 Unmanaged Cursor agent usage on engineering laptops: Open, owner named: Engineering lead.
- F6 Retrieval Provenance Gap: Open, owner named: Chief Compliance Officer.
Decisions taken
Leadership's decision on each finding, as recorded in the assessment. Findings with no decision recorded are not listed.
| Finding | Decision | Who | When | Note |
|---|---|---|---|---|
| No formal AI Acceptable Use Policy in place | Fix it | Chief Compliance Officer | 2026-05-26 | Target date |
| No sub-processor disclosure for AI vendors | Accept the risk | Chief Executive Officer | 2026-04-26 | Vendor list publishes with the Q3 privacy notice update |
Agentic Posture Findings
These findings are computed from your agent inventory posture, not inferred. Each covers one item the platform agentic terms now assign to the customer. Unknown counts as Unmet: a posture nobody has recorded is a decision nobody has made. Runtime enforcement belongs to the platform; this report records the decision and its owner.
Unauthorized subagent capability (HIGH)
- Triggered when: One or more inventoried agents can create, fork or orchestrate other agents or processes, and no authorization record (scope, approver, date) exists for that capability.
- Why it matters: An agent that can multiply itself can extend its reach beyond anything a person approved, and every action its children take is an Agentic AI Action attributable to the organization under the platform's terms. The absence of an authorization record means the organization cannot show that the resulting scope was ever decided by a person.
- Clause: AUP §14.12, Subagent Spawning Authorization
- Area: C7 AI that acts on its own is controlled. Relates to: NIST AI RMF MANAGE 2.4 (disengage or deactivate); ISO/IEC 42001 Clause 8.1 (operational planning and control).
- Owner: CISO or platform owner
- 90-day action: Inventory every agent with orchestration or spawning capability. For each, either record the authorized scope with a named approver or disable the capability. Add the authorization to the AI system register. Report the count of agents in each state at the next cadence review.
- Agents affected: Prior-authorization triage agent (Unmet)
Opaque multi-agent communication (HIGH)
- Triggered when: Agents in the inventory communicate with other agents, and that traffic is not logged, or no reviewer is named.
- Why it matters: Decisions made between agents without a reviewable record are decisions made outside human oversight, which EU AI Act Article 14 requires to be effective and which the platform's terms prohibit structuring around. Without the log, the organization cannot reconstruct how an outcome was reached.
- Clause: AUP §14.13, Agent-to-Agent Transparency
- Area: C7 AI that acts on its own is controlled. Relates to: NIST AI RMF MANAGE 2.4 (disengage or deactivate); ISO/IEC 42001 Clause 8.1 (operational planning and control).
- Owner: CISO
- 90-day action: Route agent-to-agent traffic for every multi-agent system through a logged channel with defined retention. Name a reviewer per system. Record both in the register.
- Agents affected: Prior-authorization triage agent (Unknown), Claims appeal drafting agent (Unmet)
Agent permission exceeds authorization (HIGH)
- Triggered when: An agent's provisioned permissions exceed its documented scope, or the agent has no permission record, or the agent operates under a human user's credentials.
- Why it matters: The agent can reach data and systems nobody decided it should reach. Under the platform's terms the customer is responsible for provisioning agent permissions, so an over-provisioned agent is an unmet obligation as well as an exposure.
- Clause: AUP §14.14, File and Permission Boundary
- Area: C7 AI that acts on its own is controlled. Relates to: NIST AI RMF MANAGE 2.4 (disengage or deactivate); ISO/IEC 42001 Clause 8.1 (operational planning and control).
- Owner: Identity and access management owner
- 90-day action: Provision each agent as its own identity with least privilege. Reconcile provisioned permissions to documented scope. Retire any agent running on human credentials. Record per agent.
- Agents affected: Claims appeal drafting agent (Unmet)
Agent spend without owner (HIGH)
- Triggered when: An agent can incur paid resource consumption on any platform or third-party service and has no named budget owner, or no cap.
- Why it matters: The exposure is financial and bounded by platform limits, but the organization remains liable for all charges its agents accrue, and an uncapped agent with no owner is a budget nobody is watching. Escalate to High where the agent can transact with third parties.
- Clause: AUP §14.15, Agent Spend Ownership
- Area: C6 Clear ownership and decisions. Relates to: NIST AI RMF GOVERN 2 (accountability); ISO/IEC 42001 Clause 5.3 (roles, responsibilities and authorities).
- Owner: CFO or budget owner
- 90-day action: Assign a budget owner and a cap to every spending-capable agent. Enable platform budget alerts. Add agent spend to the cadence review and to the board questions.
- Agents affected: Claims appeal drafting agent (Unknown), Medical supplies reorder agent (Unmet)
Platform terms not reflected in policy (MEDIUM)
- Triggered when: The organization deploys agents on a platform whose agentic or acceptable-use terms are not referenced in its AUP, or the terms version and review date are not recorded.
- Why it matters: The platform's terms bind the organization's agents and may require the organization to indemnify the platform for breach. A policy that does not know the terms cannot direct compliance with them, and a breach would arrive as an unplanned incident with contractual exposure.
- Clause: AUP §14.16, Platform Terms Flow-Down
- Area: C3 Agreed tools on the right terms. Relates to: NIST AI RMF GOVERN 6.1 (third-party policies); ISO/IEC 42001 Clause 8 (operation).
- Owner: General counsel
- 90-day action: For each platform hosting agents, record the terms URL, version or last-modified date, and a reviewer. Add the flow-down clause to the AUP. Add platform-terms change to the list of events that trigger a policy review.
- Agents affected: Prior-authorization triage agent (Unmet)
Regulation-anchored. Customized. Auditor-readable.
The full policy is up to 16 sections plus 3 appendices, sized to your organization, ~3,500-4,500 words, customized to the customer’s industry, jurisdictions, and frameworks. Sample shows § 1 Purpose & Scope, § 2 Definitions, § 5 Healthcare-Specific Restrictions (HIPAA-anchored, customer-specific), § 9.7 Document-Grounded AI Outputs, and § 14 Deployed Agent Policy with the § 14.9 Agent-Authored Code Governance sub-clause.
AI Acceptable Use Policy
Sample excerpt · 5 of 16 sections
Scope: Complete review, selected by Acme Health, Inc.. All twelve areas of AI governance considered.
Executive Summary
This Policy governs the use of artificial intelligence tools, agents, and embedded-AI features at Acme Health, Inc. It is anchored to HIPAA §164.502(e), §164.312, SOC 2 Common Criteria CC5.3 and CC7.2, GDPR Articles 28 and 35, the EU AI Act (Articles 13, 14, 50, 52 — with Article 4 AI literacy in force since February 2, 2025 (as amended by Regulation (EU) 2026/1744: measures that support AI literacy, no fixed level per person), Article 50 transparency effective August 2, 2026, and the high-risk regime moved to December 2, 2027 for standalone Annex III systems and August 2, 2028 for embedded Annex I systems per the 2026 Digital Omnibus), and the NIST AI Risk Management Framework. The Policy applies to all employees, contractors, and agents acting on Acme Health's behalf. The full Policy contains 16 sections plus 3 appendices; this excerpt shows § 1, § 2, § 5, § 9.7 and § 14.
Section 1: Purpose and Scope
1.1 Purpose
This Policy establishes the rules under which artificial intelligence (AI) tools may be used by Acme Health, Inc. ("Acme Health" or "the Company") personnel in the course of their work. AI tools are powerful and increasingly pervasive; their use creates legal, regulatory, contractual, and reputational risks that are categorically different from those posed by traditional information technology.
This Policy exists to manage those risks while preserving the productivity and innovation benefits AI tools provide.
1.2 Scope
This Policy applies to:
- All employees, contractors, consultants, and temporary staff acting on Acme Health's behalf
- All AI tools, including but not limited to: generative AI (text, code, image, audio, video), AI assistants, AI agents, autonomous-agent frameworks, AI features embedded in business applications, and AI-enabled browser extensions
- All Acme Health information systems and any personal devices used to access Company data
- All Acme Health data, customer data, employee data, vendor data, and third-party data the Company processes
1.3 Effective Date
This Policy is effective 2026-05-01 and supersedes any prior AI use guidance issued by Acme Health.
Section 2: Definitions
For the purposes of this Policy:
AI Tool — Any software product or service that uses machine learning, natural language processing, or generative artificial intelligence to produce text, code, images, audio, video, recommendations, classifications, or other outputs.
AI Agent — An AI tool that operates with a degree of autonomy, including the ability to use other tools, call APIs, retrieve data, take actions, or coordinate with other agents.
Embedded AI — AI features built into a business application (Microsoft 365 Copilot, Google Workspace Gemini, Salesforce Agentforce, Notion AI, etc.) where the AI inference is proxied through the SaaS vendor's own infrastructure.
Sanctioned AI Tool — An AI tool that has been reviewed and approved for specific use cases per the AI Tools Registry maintained by the CISO's office (Appendix A).
Confidential Information — Acme Health business information that is not public, including personnel records, customer lists, financial data, source code, product roadmaps, and contractual terms.
Restricted Information — Acme Health information subject to specific legal, contractual, or regulatory restrictions, including Protected Health Information (PHI) under HIPAA.
Section 5: Healthcare-Specific Restrictions (HIPAA Compliance)
Because Acme Health processes Protected Health Information (PHI) as defined under HIPAA, the following additional restrictions apply to any AI tool used in connection with patient data, clinical operations, or revenue cycle management:
5.1 Business Associate Agreement Required
No AI tool may process PHI without a Business Associate Agreement (BAA) executed with the AI vendor that explicitly includes the AI service as in-scope. This includes embedded-AI features such as Microsoft 365 Copilot, Google Workspace Gemini, and Salesforce Agentforce — the underlying enterprise BAA does not automatically extend to AI features.
5.2 Prohibited Embedded-AI Configurations
Until a Copilot-specific BAA addendum is executed and the data flow is documented, the following Microsoft 365 Copilot configurations are PROHIBITED on the Acme Health tenant:
- Copilot indexing of any SharePoint site or OneDrive folder containing PHI
- Copilot summarization of any Outlook conversation containing PHI
- Copilot transcription or summarization of Teams meetings discussing PHI
5.3 Patient-Facing AI Disclosure
Per HIPAA §164.520 (Notice of Privacy Practices) and applicable state law, any AI tool that interacts directly with a patient (chatbot, intake assistant, AI scheduler) must be disclosed in the Notice of Privacy Practices and any patient-facing consent forms. The disclosure must specify what AI is used for, what data it accesses, and what controls govern that access.
5.4 Clinical Decision Support
AI tools used to support clinical decisions are subject to additional governance under § 164.312(c)(1) (integrity controls) and the FDA's Software as a Medical Device (SaMD) guidance where applicable. Clinical decision support tools require executive sign-off from the Chief Medical Officer in addition to the CISO.
5.5 Sub-Processor Disclosure
Per GDPR Article 28 (where applicable to EU-resident patient data) and customer DPAs, the AI sub-processor list maintained at acmehealth.example/trust must be updated within 30 days of any new AI vendor onboarding. Customers retain the right to object to a new sub-processor and have 30 days from notification to do so.
Section 9: Security Requirements (excerpt: § 9.7)
9.7 Document-Grounded AI Outputs
Where an AI assistant answers from Acme Health documents and the answer feeds a filing, a contract decision, a compliance determination or a consequential decision, the answer must carry the document, version and page or section it relied on, and the reviewer must check the cited location before use. An answer with no source location is not evidence.
Section 14: Deployed Agent Policy
14.1 Scope
This Section applies whenever Acme Health deploys, builds, hosts, or integrates an AI agent — including no-code agents created in platforms such as Microsoft Copilot Studio, Salesforce Agentforce, Gemini Enterprise custom agents, or ServiceNow Agentic AI — and whenever Acme Health consumes Model Context Protocol (MCP) servers or participates in agent-to-agent (A2A) discovery chains.
14.2 Agent Registration
Every agent Acme Health deploys must be registered in the agent inventory maintained by the CISO's office before it is enabled in production. Registration captures: agent name, owner, hosting platform, declared tools and skills, identity model, data classes the agent is permitted to access, and the application boundary the agent operates within.
14.3 MCP Server Allowlist
Acme Health maintains a vetted allowlist of permitted MCP servers. Connecting an agent to any MCP server not on the allowlist is prohibited. The allowlist is reviewed at the same cadence as the AI Tools Registry. Allowlisted MCP servers are subject to re-validation at minimum quarterly to detect Discovery Poisoning.
14.7 Kill-Switch
Every deployed agent must be subject to a documented kill-switch — a single action by the CISO's office (or designee) that immediately disables the agent across all environments. The kill-switch procedure is tested quarterly.
14.9 Agent-Authored Code Governance
Where Acme Health engineering teams use coding agents that author production code (Cursor, Claude Code, Google Antigravity, Gemini CLI, GitHub Copilot Workspace, or equivalent), the following controls apply: (a) policy provenance — the coding agent's policy and security context must be documented; (b) named human accountability — every agent commit, PR, or deployment must carry a named human owner; (c) change-management evidence — coding agents must operate within the same code review and CI/CD gating as human-authored code; (d) runtime IAM separation — the runtime IAM the coding agent holds at authoring time must be distinct from the runtime IAM the deployed code itself runs under; (e) validator-pair attestation — where a coder-validator agent pair is used, the validator's attestations are recorded as evidence but do not substitute for the human accountability requirement.
14.12 Subagent Spawning Authorization
Rule. No AI agent operated by or on behalf of Acme Health may create, duplicate, fork or orchestrate another agent, subagent or process beyond the scope for which it was authorized, unless a named individual has given explicit prior authorization for that scope and the authorization is recorded. Agents authorized to orchestrate others carry a documented maximum scope, and any agent they create inherits no permission its parent was not granted.
Anchor. Google Cloud Agentic AI Responsible Use Guidelines, Section 2 (explicit Customer authorization before agents "create duplicate agents, subagents, or forked processes that would reasonably be expected to exceed Customer's intended scope of action"); EU AI Act Article 14 (effective human oversight); ISO/IEC 42001 Clause 6.1 (actions to address risks).
Owner. CISO, or the platform owner designated in Appendix A.
Record. For each orchestrating agent: the authorized scope, the approver, the date, and the review date. Maintained in the AI system register.
Enforcement. Runtime restriction of spawning and orchestration is the function of the agent platform and its permission model. This policy records the authorization; it does not perform the restriction.
14.13 Agent-to-Agent Transparency
Rule. Where agents communicate with other agents, Acme Health does not structure, configure or permit that communication in a way that places agent decisions outside the review of the accountable human owner. Agent-to-agent traffic that influences an action affecting people, money, data or legal position is logged in a form the owner can review, and the owner is named.
Anchor. Google Cloud Agentic AI Responsible Use Guidelines, Section 4 (agentic technologies should not be used "as part of a multi-agent system to obfuscate agent-to-agent communications as a means to bypass human oversight"); EU AI Act Article 14 (effective human oversight).
Owner. CISO.
Record. The logging location, the retention period, and the named reviewer for each multi-agent system in the register.
Enforcement. Logging and observability tooling. This policy sets the requirement and names the reviewer.
14.14 File and Permission Boundary
Rule. No agent alters files, bypasses file permissions, or extends its own access without explicit prior authorization from a named individual. Every agent is provisioned as its own identity with the least privilege its authorized scope requires, by a named owner, and its permissions are reviewed on the program cadence. Agents do not operate under a human user's credentials.
Anchor. Google Cloud Agentic AI Responsible Use Guidelines, Section 2 (explicit Customer authorization before agents "alter files or bypass file permissions") and Section 5 ("You are responsible for provisioning appropriate agent permissions"); ISO/IEC 27001 Annex A 5.15 (access control) and 8.2 (privileged access rights).
Owner. Identity and access management owner.
Record. Per agent: identity, provisioned permissions, authorized scope, owner, last review date.
Enforcement. Platform identity and access management and runtime access controls.
14.15 Agent Spend Ownership
Rule. Every agent able to consume paid resources on any platform or third-party service has a named budget owner and a spending cap. Acme Health treats charges incurred by its agents as its own, reviews agent spend on the program cadence, and reports material variances to the accountable executive.
Anchor. Google Cloud Agentic AI Responsible Use Guidelines, Section 4 (agent resource consumption listed as high-impact, "as you remain liable for any charges accrued by your agents"); SOC 2 CC6.1 (logical access controls).
Owner. CFO or the budget owner designated in Appendix A.
Record. Per agent: budget owner, cap, platform, review date.
Enforcement. Platform quotas and budget alerts.
14.16 Platform Terms Flow-Down
Rule. Agents Acme Health deploys on a third-party platform comply with that platform's acceptable use policy and any agentic-AI terms the platform publishes. Acme Health records, for each platform, the terms version its agents are bound by and the date it was last reviewed. Because Acme Health may be required to indemnify the platform for its agents' breach, a breach of platform terms by an agent is treated as a reportable incident under Acme Health's incident process.
Anchor. Google Cloud Terms of Service, Sections 3.3 and 13.2 (last modified October 12, 2026: use restrictions apply to "any AI Agent"; customer indemnity for use of the Services or AI Agents "in breach of the AUP or Section 3.3"); Google Cloud Service Specific Terms, Section 19(b) (Google disclaims liability and indemnity for Customer AI Agents and Third-Party AI Agents).
Owner. General counsel.
Record. Per platform: terms URL, version or last-modified date, review date, reviewer. Maintained in the AI system register alongside the agents deployed there.
Enforcement. Contractual. Operational compliance is enforced by the platform's own controls; Acme Health's duty is to know the terms, reflect them in policy, and respond to breach.
Appendices
Appendix A: Approved AI Tools Registry (sample excerpt)
The full registry is maintained by the CISO's office. The excerpt below is illustrative of the format.
| Tool | Category | Approved Use Cases | Data Class Limit | Approved | Review |
|---|---|---|---|---|---|
| Microsoft 365 Copilot | Embedded productivity | Document drafting (non-PHI), meeting summarization (non-PHI) | Confidential (non-PHI) | 2026-05-15 | 2026-11-15 |
| Notion AI | Embedded knowledge | Knowledge-base search, document summarization | Confidential | 2026-04-01 | 2026-10-01 |
| Cursor | Direct developer tool | Code authoring with mandatory PR review; agentic features DENIED until § 14.9 controls in place | Confidential (no customer identifiers) | 2026-04-15 | 2026-07-15 |
| ChatGPT Enterprise | Direct conversational | Research, drafting, brainstorming (no Restricted data) | Confidential (no PHI) | 2026-04-01 | 2026-10-01 |
Same data, different artifact, different audience.
Derived from the same audit as § 01 above. CEO voice (first-person plural), plain English, no jargon, no CEL or SPIFFE acronyms. The document a CEO actually hands up to the board audit committee — the Executive Risk Report stays in the CISO’s briefcase as the supporting detail.
Board Memo — AI Governance Risk
Acme Health, Inc.
Scope: Complete review, selected by Acme Health, Inc.. All twelve areas of AI governance considered.
Who this is for: Your board of directors. What it answers: What AI risk the organization carries today, what leadership has decided, and what the board is asked to note.
To the Board of Directors and Audit Committee of Acme Health
We have completed a comprehensive review of our artificial intelligence risk posture and identified a high level of exposure that requires immediate attention. Our most significant concern is the unmanaged use of Microsoft 365 Copilot within our digital environment that contains protected health information. Currently, this tool is active without the necessary policy safeguards or specific legal agreements required for healthcare data. This creates a situation where a single configuration change could trigger a mandatory data breach notification under federal law. The lack of a formal acceptable use policy for AI tools also threatens our upcoming security audit certifications. We are taking decisive action to pause these services until we have established the proper governance, legal disclosures, and employee training to ensure we utilize these technologies safely and remain in full compliance with healthcare privacy regulations.
What we found
- We discovered that Microsoft 365 Copilot is active on our primary data systems and accessing protected health information without the required HIPAA business associate agreements or usage policies in place.
- Our engineering team is using an AI coding assistant called Cursor that may be transmitting sensitive source code and customer identifiers to external providers without proper data protection oversight.
- We currently lack a formal AI Acceptable Use Policy and a public list of AI sub-processors, which will result in a failure to meet our SOC 2 audit requirements and international data privacy obligations.
- Leadership has recorded a decision on 2 of 11 findings (1 to fix, 1 accepted); 9 have no decision yet.
What we are doing
- Within the first week, our Chief Information Security Officer is disabling Copilot across the entire organization until we have adopted formal safety policies and executed the necessary business associate agreements.
- By the second week, our Legal team will implement a new AI Acceptable Use Policy to provide clear rules for how our employees interact with these tools, with sign-off from the CISO, General Counsel, and CEO.
- By the fourth week, our Legal team will publish a formal disclosure of all AI vendors we use and notify enterprise customers, ensuring we meet our transparency requirements for regulators and contractual obligations to the business.
Each action in the Executive Risk Report's 90-day plan names the finding it closes.
I welcome the Board's questions regarding these remediation steps at our next session.
One page your broker can place in the underwriting file.
A one-page renewal summary of the documents above: which AI tools and agents are in use, what agents may do, what changed since the last summary, and five questions for the renewal conversation. Built from the assessment, with no model call; each source document can be checked at its verification URL. This sample compares against a previous summary file, so the “What changed” section is populated.
It reports what is recorded. It is not an opinion on coverage, pricing or compliance. The approach follows the standing one-page brief recommended in MITRE and Mosaic Insurance, The New Economics of Cyber Risk, 2026.
AI Posture Summary · for the cyber insurance renewal of Acme Health, Inc.
| Source document | Short ID | Date | Verification |
|---|---|---|---|
| Executive Risk Report | sample-err | 2026-10-22 | https://sanctumshield.com/verify/sample-err |
| AI Acceptable Use Policy (version 2) | sample-aup | 2026-10-22 | https://sanctumshield.com/verify/sample-aup |
| Board Memo | — | 2026-10-23 | derived from the Executive Risk Report sample-err, verified at that record |
1. What changed since the last summary
Two AI tools were added (Perplexity and Zoom AI Companion). One posture item changed: the Medical supplies reorder agent moved from Unknown to Met on own identity, least privilege. One high-severity finding was closed. The Board Memo was refreshed on October 23, 2026.
2. AI in use
Inventory last updated October 22, 2026, by import.
3. Agent posture
| Agent | Platform | Can act | Subagent spawning | Agent-to-agent log | Own identity, least privilege | Spend owner and cap | Platform terms in AUP |
|---|---|---|---|---|---|---|---|
| Prior-authorization triage agent | Google Cloud | No | Unmet | Unknown | Met | Met | Unmet |
| Claims appeal drafting agent | Microsoft Copilot Studio | No | Met | Unmet | Unmet | Unknown | Met |
| Medical supplies reorder agent | In-house | Yes | Met | Met | Met | Unmet | Met |
4. Governance in place
- AI Acceptable Use Policy version 2, October 22, 2026, with the Persuasion-Exposure Validation controls.
- Executive Risk Report, October 22, 2026: 1 critical, 8 high, 4 medium, 0 low findings open.
- Board Memo, October 23, 2026.
- AI Governance Coach available to staff by voice and text, included in the platform plan.
5. Five questions for the renewal conversation
- Do we have a current inventory of the AI tools and agents in use, and when was it last updated? Yes. Inventory last updated October 22, 2026, by import.
- Which agents can act on our behalf (transact, send, write or change records), and is each one's permission approved and dated? One agent can act on the organization's behalf. One has its own identity and least-privilege permissions recorded as Met.
- What is our record of closing AI governance findings since the last summary? One high-severity finding was closed.
- Which AI capabilities do we run that we did not build, including AI embedded in existing software? Three products with embedded AI, and five of the six AI tools in use are third-party (one is built in-house; one is not yet rated).
- Is our AI use policy current, and when was it last reviewed by leadership? Version 2 issued October 22, 2026. Board Memo prepared October 23, 2026. Board review: not yet recorded.
6. How to use this summary
Share it with your risk manager or broker ahead of renewal, ideally once a quarter. Paper 3 of MITRE and Mosaic Insurance's series The New Economics of Cyber Risk recommends a standing one-page brief and a posture update in the underwriting file so that improvement shows up as a track record. This summary is the AI section of that brief. Create a new one after each re-run and keep the data file; the next summary will show what changed.
Verification record: https://sanctumshield.com/verify/sample-posture
Can you name the system’s owner, point to the line in your AI system register where it sits, and say what it may not decide on its own? Wherever the answer is not yet, that is where the record begins.
These are the questions a director can ask about any AI system a company runs. Each one has an answer, and the answer lives in one of the artifacts above.
| # | The board’s question | Where it is answered |
|---|---|---|
| 1 | What is this system allowed to do: recommend, decide, act, spend, speak for us? | AI Acceptable Use Policy — authority and scope |
| 2 | What is it not allowed to do, and who signed that list? | AUP — the one-page not-allowed list, named signer |
| 3 | Who can override it, and how fast? | AUP — override and escalation |
| 4 | What evidence has to sit behind an output before anyone acts on it? | AUP — evidence and human-review requirements |
| 5 | If it goes wrong, can we reconstruct what happened? | Executive Risk Report — record-keeping findings; Verification URL, dated and third-party-verifiable |
| 6 | Who tests it, independently of the people who built or bought it? | Executive Risk Report — assessment method; monthly cadence |
| 7 | What makes it stop, or hand back to a person? | AUP — stop and escalation triggers |
| 8 | Who is accountable for the outcome, by name? | Board Memo — accountable owner; AUP — responsibility assignments |
| 9 | Can we show that the action an agent executed is the one that was authorized? | Runtime controls, below the artifact layer — a per-action record linking the authorization (who, under which policy version, when) to the executed action, produced by the enforcement or observability layer. SanctumShield's artifacts record which policy was in force, who owned it, and when it was last reviewed; they do not observe individual agent actions. A buyer needs both: ask the runtime vendor for the first and SanctumShield for the second. |
| 10 | Who owns what our agents spend, and what is the cap? | AUP §14.15, agent spend ownership; Executive Risk Report, the agent spend without owner finding |
Four artifacts. Every question above, answered out loud. Refreshed on a monthly cadence, because the next question is always “and is that still true?”
A policy tells people what they should do. Architecture can stop some things from happening. Neither can testify. The dated record is what a regulator or an underwriter reads. For the renewal file, the AI Posture Summary below is the one-page view of all four.
Generate your own — for your company, department, or line of business.
Same artifacts, customized to your industry, jurisdictions, frameworks, and AI tool inventory. Run the free Shadow AI Check first to see the assessment style; the full subscription produces all three deliverables (plus the verification URL) in minutes from a guided assessment.