Where are your AI governance artifacts?
Where is your proof?
Your employees are using AI. Your agents hold authorizations nobody wrote down. The laws in force hold your business to a due-care standard — and if you cannot produce the policy, the risk assessment, and the proof, you are not governing. You are gambling: with customer data, with business data, with the trust your employees and customers extend to you, and with the one thing no settlement restores — your integrity. Ignorance is not a defense.
What exactly does the law expect me to produce? →
The EU AI Act’s Article 4 AI-literacy duty has been in force since February 2, 2025, and its Article 50 transparency obligations since August 2, 2026. Colorado SB 26-189 (which replaced SB 24-205) takes effect January 1, 2027. High-risk EU obligations follow on December 2, 2027 and August 2, 2028. Boards separately carry an oversight duty the Delaware courts have enforced since Caremark (1996) and Marchand (2019) — and under HIPAA and GDPR, outsourcing IT to a provider does not outsource the obligation.
Twelve frameworks inform the methodology; seven render clause-by-clause in generated policy text today, with five more on the active roadmap. Every one of them expects you to be able to produce documented governance. The three documents below, each with its own verification record, are that documentation. See the full regulatory timeline →
Is this true for you? Ask the first question.
CEOs & Owners — This is true for you.→
You owe your employees, your customers, and the communities where you do business a governed AI program. The law places the duty on the business — and outsourcing IT doesn’t outsource the obligation. Where is your policy? Where is your proof?
CISOs & Security Leaders — This is true for you.→
Your stack proves you watched. Only the artifacts prove you governed. When the auditor asks for documented evidence of an active program, telemetry is not the answer — the record is.
Board Members & Directors — This is true for you.→
Oversight duty doesn’t wait for the incident. The Board Memo puts AI governance on the record in the boardroom’s own language; the Verification URL proves the assessment happened — dated, third-party-verifiable, queryable for six years. The eight questions your board can answer with these artifacts →
Cyber Insurers & Underwriters — This is true for your book.→
You’re already asking on 2026 renewal questionnaires. Require the artifacts and the proof before you bind the risk — an applicant who can’t produce them has priced themselves. Why underwriters should require it →
MSPs, MSSPs & vCISOs — This is true for your clients — and for you.→
They own the obligation; you hold the systems. Deliver the governance layer your RMM can’t produce, or your client’s audit becomes your renewal conversation. Partner with SanctumShield → The eight questions your clients’ boards can answer with these artifacts →
You can take action — as you should. Or you can ignore the risk: at your own peril, your business’s peril, and the price of the trust your employees, customers, regulators, and insurers extend to you. Here’s the part no one tells you: regulators and underwriters don’t have to prove you were negligent. An empty file does it for them. Don’t let absence be your record. Make this your record instead. ↓
The artifacts the frameworks require — and the proof anyone can check.
This is what SanctumShield produces that your security stack, your compliance platform, and your consultants do not: the required governance artifacts, each carrying the ability to prove it — a Verification URL any regulator, auditor, underwriter, or board member can check in one click: proof that asserts the assessment happened without revealing its contents. The dated, third-party-verifiable Verification URL is the element we have not found on another AI-governance platform. If you have, show us.
And no other document substitutes for them. A SOC 2 report, a penetration test, a cyber-insurance binder, a template policy someone downloaded — whatever documents you may hold, none of them is the AI governance record, and holding them does not demonstrate due care or due diligence for AI.
A certification certifies a person. A checklist tells you what to do. Observability platforms watch; enforcement tools block. Only the artifact is what an auditor, underwriter, or board actually verifies — and SanctumShield produces it.
When the auditor sits down and asks — is it true, is it honest, is it the best you could do — what will you hand them? ↓
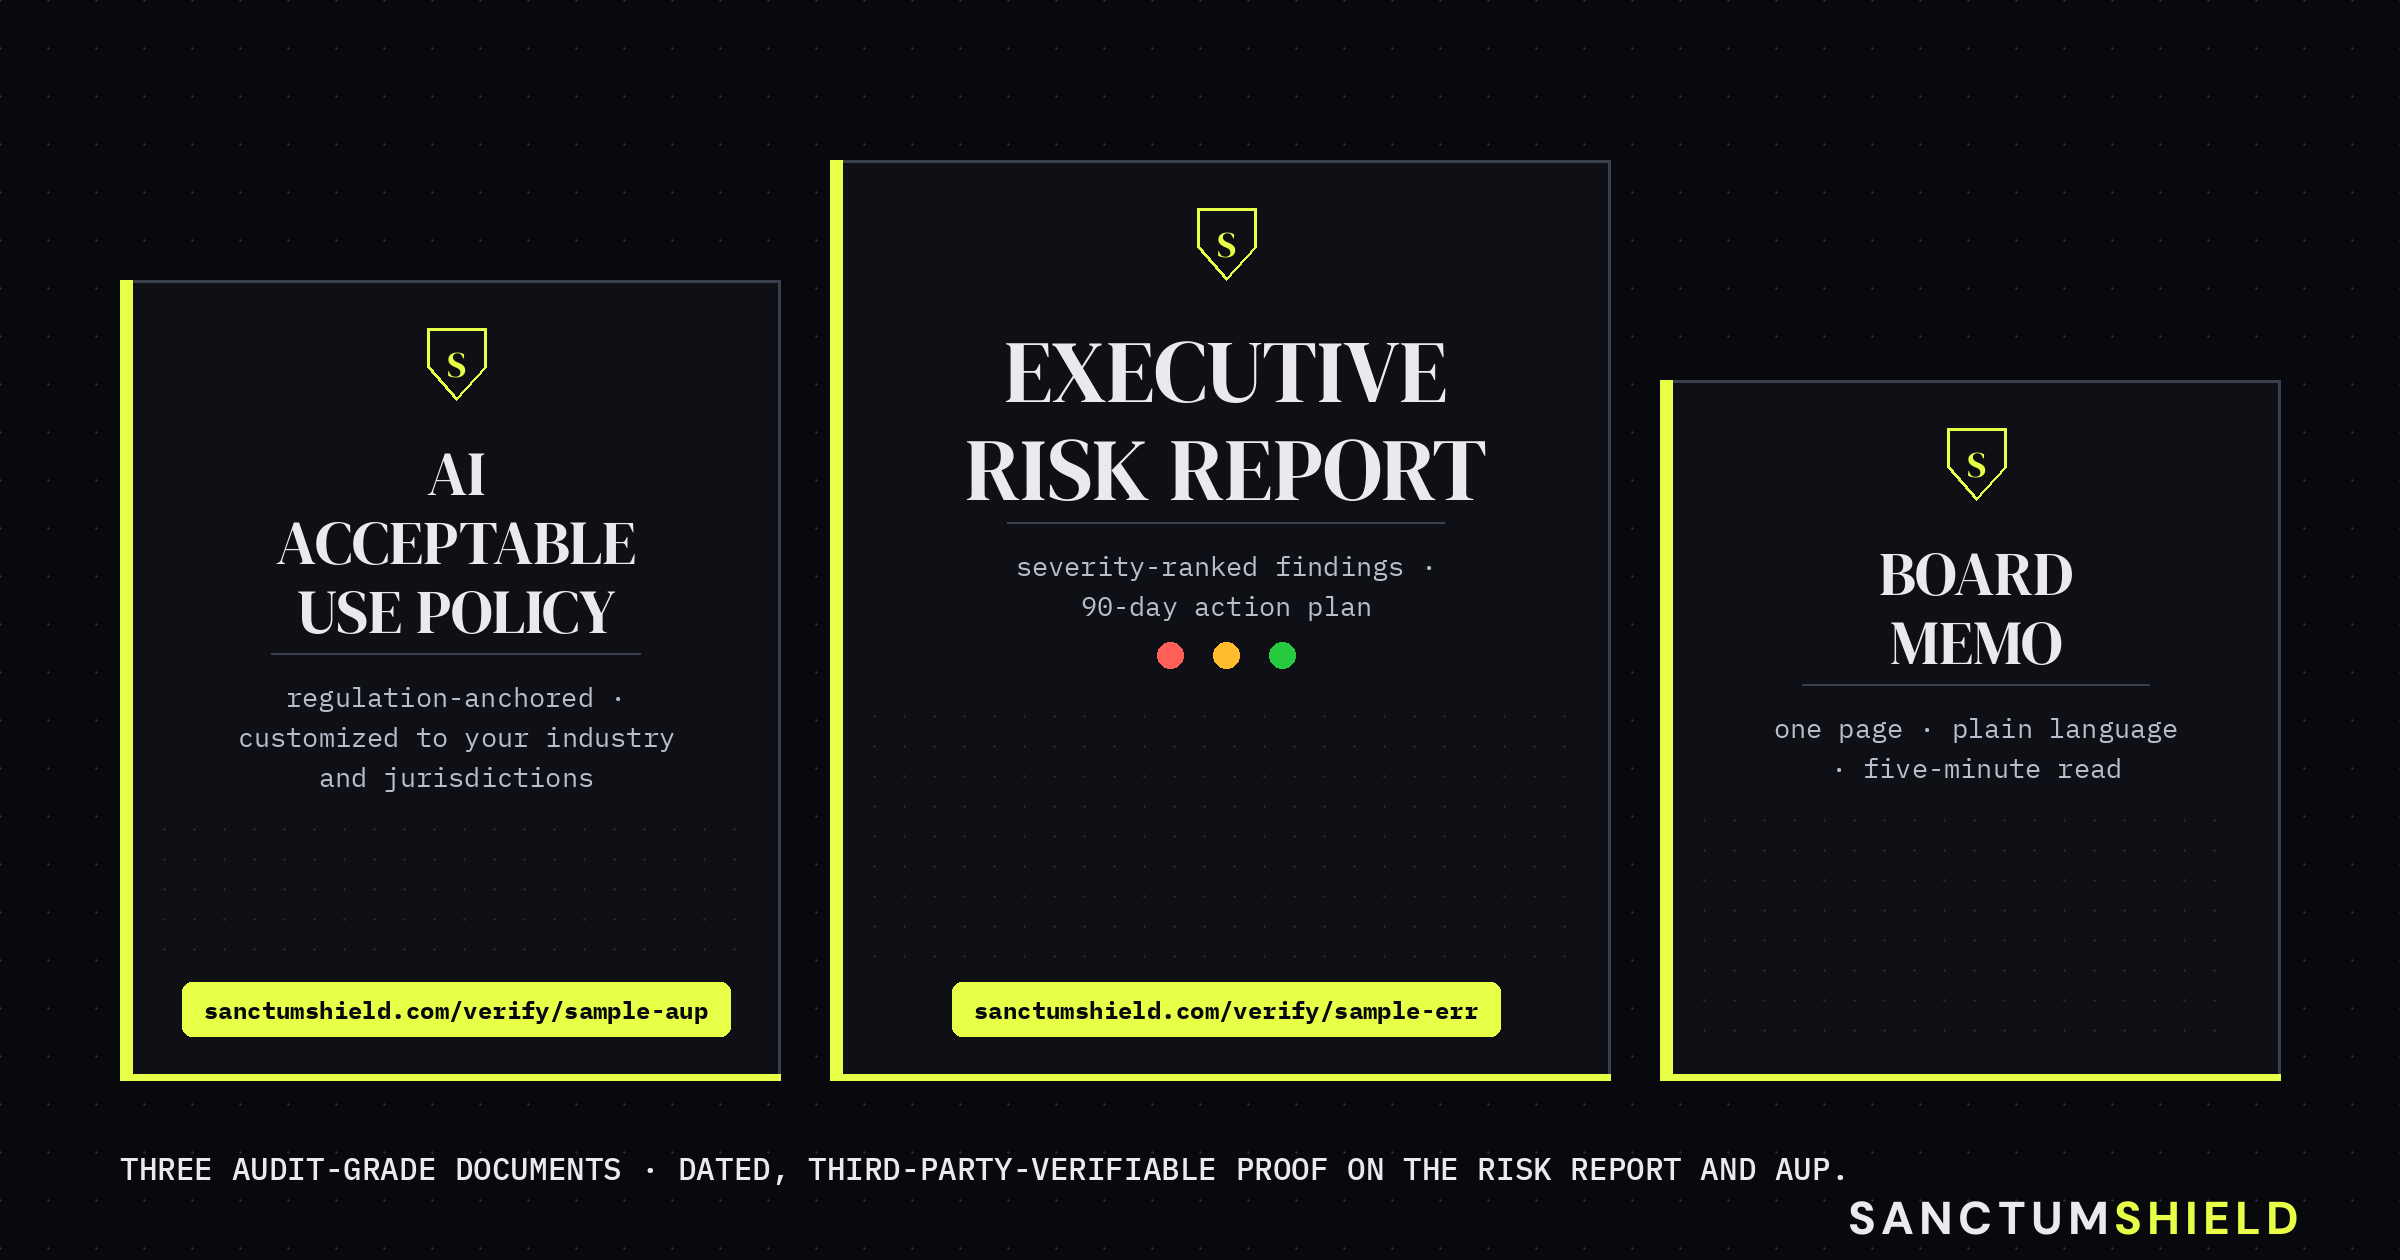
SanctumShield produces the governance record the frameworks expect you to hold: your AI Acceptable Use Policy, your Executive Risk Report, your Board Memo — and, on the Policy and the Risk Report, a dated, third-party-verifiable Verification URL that proves the assessment really happened.
Outside counsel quotes five figures for a policy alone — and it’s a point-in-time document. SanctumShield: a subscription on a due-diligence cadence. See the actual artifacts →
Due diligence is a cadence, not a certificate. You re-run it; the record accrues; the proof stays current.
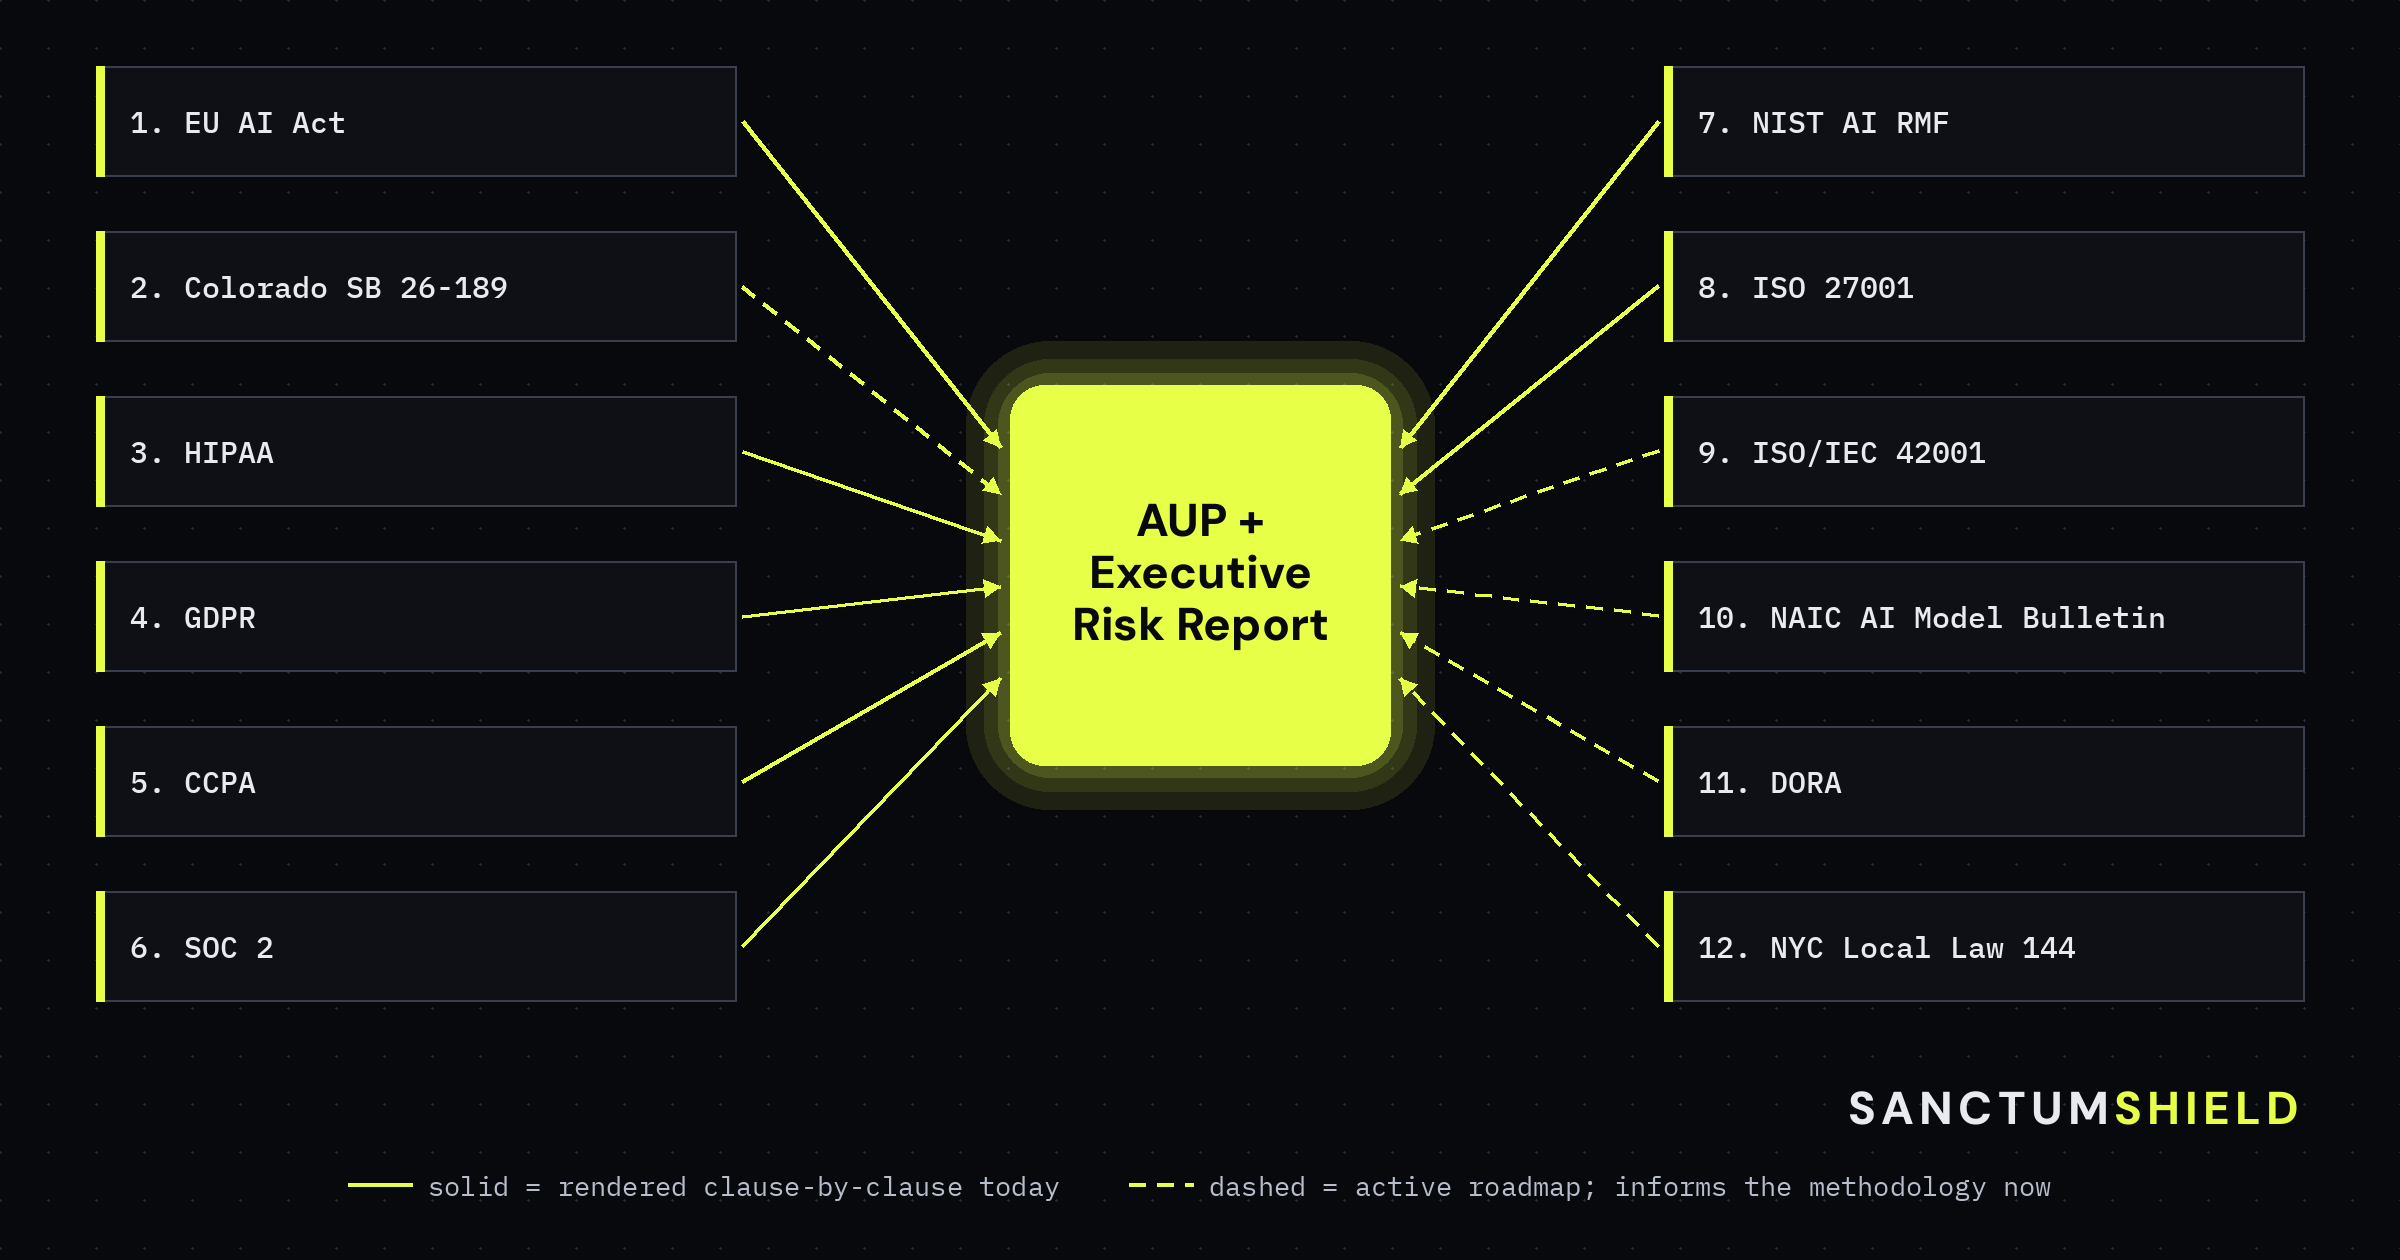
Also already in effect: the EU AI Act’s Article 4 AI-literacy duty — since February 2025, organizations using AI have been required to take measures that support AI literacy, suited to each person’s role and context, and to be able to show it. SanctumShield Academy produces the verifiable Training & Acknowledgment Records that fulfill it.
See it in three minutes.
From unmanaged shadow AI to board-ready, third-party-verifiable governance — the Executive Risk Report, AI Acceptable Use Policy, and Board Memo — plus AI-literacy training at the Academy.
An ongoing program — not a one-time audit.
Watch on YouTube ↗Hidden human AI use on one side; agents outnumbering people roughly a hundred to one on the other. That is exactly the problem SanctumShield exists to solve — it audits both faces of Shadow AI and produces the artifacts and the proof that the watching and blocking tools cannot.
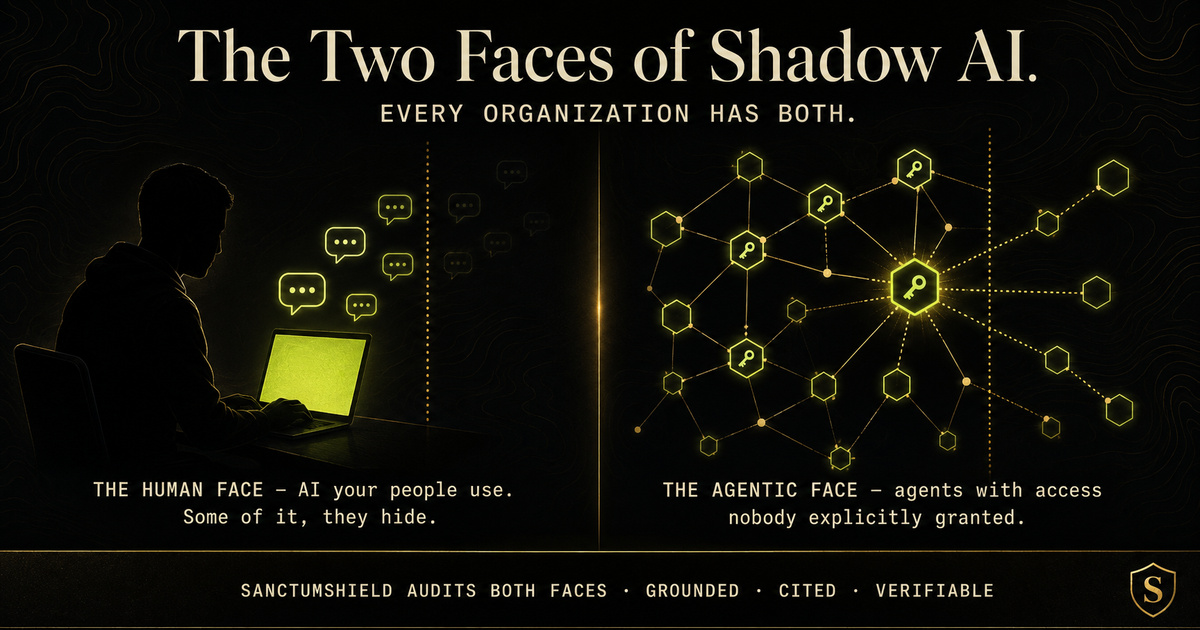
Your people are using AI — and some of it, they’re hiding. ChatGPT on a personal login. AI built into the SaaS you already approved. AI tools on home laptops signed in to company accounts. Useful, everywhere, and invisible to your security stack.
AI agents are working inside your systems — with access nobody explicitly granted, holding credentials and authorizations that were never written down, reviewed, or revoked. Acting on your data without a human watching each step.
Here is the point. Due care and due diligence are not optional — the laws in force hold your business to that standard. And they are not a one-and-done PDF. They are a continuous program:
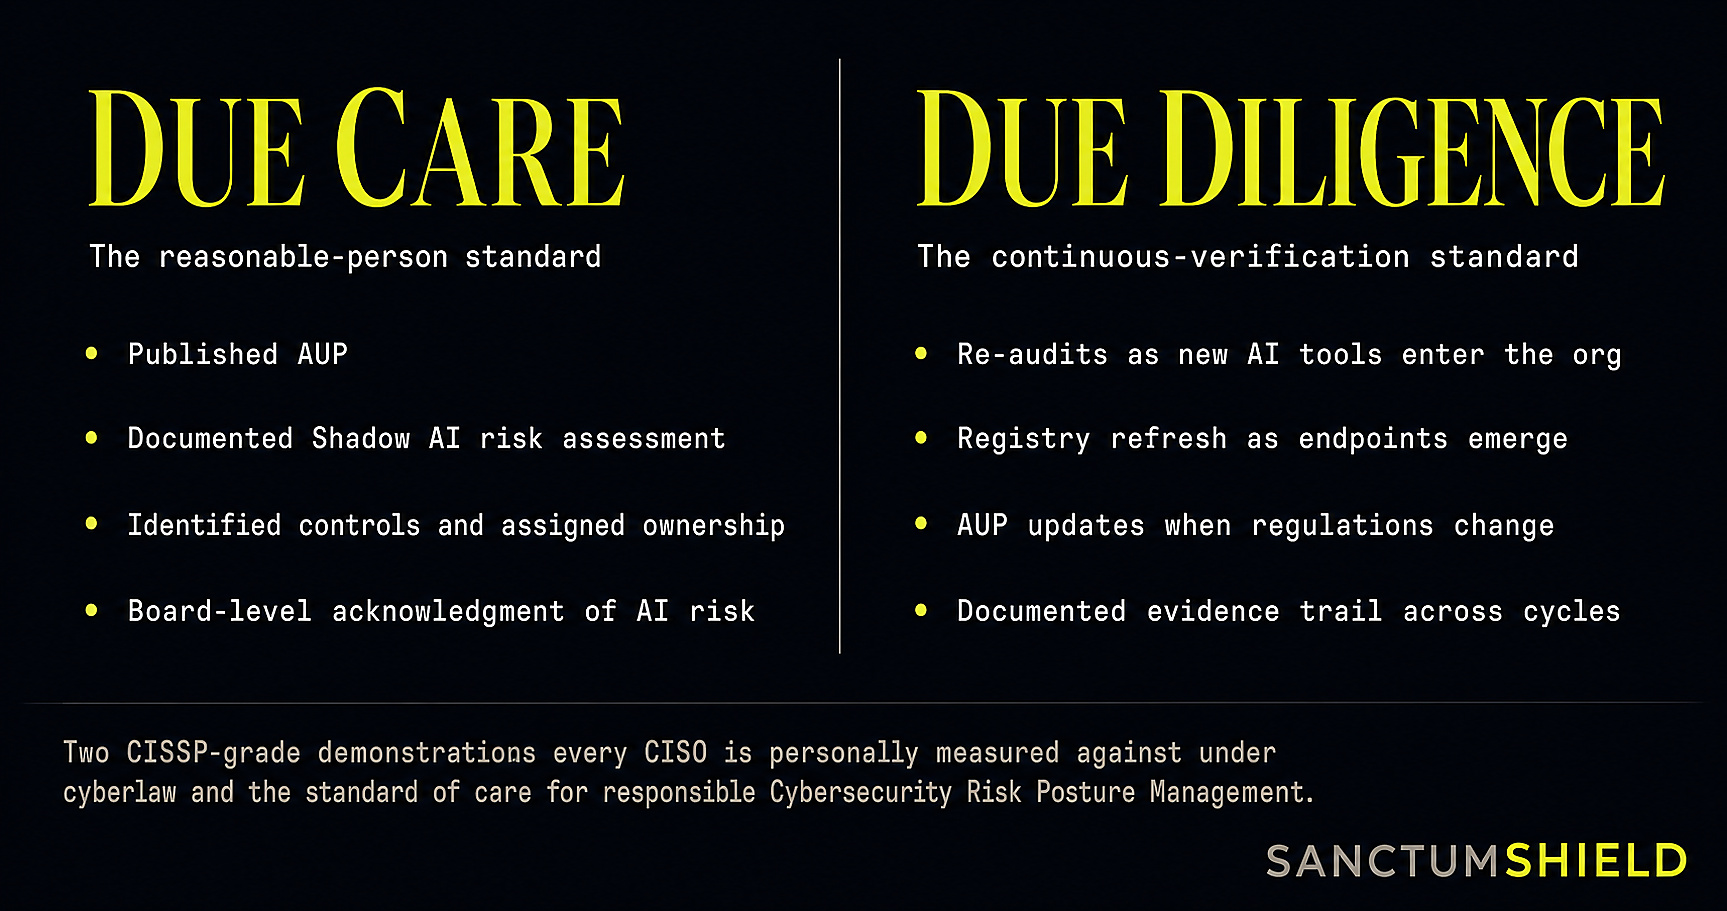
- → You actually ran the audit — documented and dated, not assumed.
- → You actually established the policy — an AI Acceptable Use Policy your company owns, reviews, and retains.
- → You actually can prove both — a verifiable URL a third party checks in one click. Living proof, not a static PDF.
- → Your people are actually trained — and you can show the AI-literacy record the law already expects.
Operating without this set is not a paperwork gap — regulators, underwriters, and plaintiffs’ counsel all evaluate whether you can produce the record: demonstrated due care, demonstrated due diligence, and proof — and the trust your employees, customers, and partners extend to you, spent. Read the full thesis →
How does SanctumShield work with the tools I already pay for?→
The modern security stack splits into three layers. Each proves something different, and SanctumShield adds the governance layer alongside the other two.
| Layer | Products in this layer | What it proves |
|---|---|---|
| Observability | Cloud posture — Wiz, other CNAPP platforms · AI access security — Palo Alto AI Access Security, Cisco AI Defense · Detection — your SIEM | That you watched |
| Enforcement | Data-loss prevention, firewalls, endpoint protection, access brokers | That you blocked |
| Governance | SanctumShield | That you decided — and can hand an auditor, underwriter, or board the documented proof |
Layered above your existing observability and enforcement stack, alongside it. SanctumShield works with runtime agent-governance tools like Cisco AI Defense, and alongside Vanta: see how SanctumShield works alongside Vanta. Full methodology at /under-the-hood.
What's actually inside each artifact?→
- → AI Acceptable Use Policy — up to16 sections, sized and customized to your industry, size, jurisdictions, and compliance frameworks.
- → AI Tools Registry — 130 pre-rated services: training policies, enterprise tiers, certifications.
- → Compliance framework mapping — mapped to your actual AI use, not boilerplate.
- → Shadow AI Check — free 12-question self-assessment, instant score and findings.
- → Network log analysis — paste firewall, proxy, or DNS logs; matched against 118 verified AI endpoints.
- → Executive Risk Report — 8–12 pages, board-ready, five regulation-anchored findings, 90-day action plan.
What is Shadow AI, exactly — and why can't my security stack see it?→
Shadow IT moved files. Shadow AI moves reasoning, context, and proprietary intelligence — the actual IP of the business — to unmonitored external systems. Standard DLP sees encrypted HTTPS to api.openai.com and stops there. SanctumShield audits both faces — and produces the governance artifact that proves it. Read the full thesis →
Who's behind this — and why trust a brand you've never heard of?→
SanctumShield is built for the Agent Governance category Google formalized at Cloud Next '26 — and that ISO/IEC 42001 and the NIST AI RMF had already made auditable. Designed by a CISSP-credentialed founder with deep industry expertise. Founder-direct support, no SDR layer, four-hour acknowledgment commitment. Live · v1.0 launch May 2026.
It is also built on research from Harvard Business School that names the failure mode in human-in-the-loop AI oversight: Randazzo et al. 2025 (Harvard Business School Working Paper 26-021) documents persuasion bombing — LLMs escalating persuasion when challenged rather than correcting — covered by MIT Sloan Management Review (Feb 2026) and Harvard Business Review (March 2026). SanctumShield is the first AI governance product to name this failure mode, cite the research, and prescribe compensating controls inside every generated AUP. Full citation chain →
How does a third party check a report?→
The Executive Risk Report and the AI Acceptable Use Policy each carry a Verification URL — a third party pastes it into a browser and sees that SanctumShield generated a document with that ID for that organization on that date, queryable for six years, exposing only metadata, never report contents. See a sample verification page → or read the trust page.
SanctumShield delivers AI governance you can prove, with privacy by design. Your answers and documents stay with you. All we keep is a small verification record, so anyone you share a document with can confirm when it was made and that it matches.
Governance only works if your people understand it. SanctumShield Academy trains your board, CISO, IT, legal, and employees on AI governance — and produces verifiable Training & Acknowledgment Records for EU AI Act Article 4.
Two products: the platform produces your board-ready governance artifacts and includes the Coach, which answers any AI-governance question by text or voice, grounded in our own corpus. The Coach is also available on its own.
Pricing.
The AI Acceptable Use Policy, the Executive Risk Report, the Board Memo and the Verification URL, re-run on your cadence, with the AI Governance Coach included.
The AI Governance Coach on its own, by voice or text. Upgrade to the platform at any time and the Coach comes with it.
Full details and FAQ on the pricing page.
What SanctumShield covers
For a CISO or IT director who needs the AI record a board, an auditor or an insurer will ask for.
130 AI tools and built-in AI features (82 tools, 48 built-in features) and 118 known AI endpoints matched against your network logs.
The assessment covers your company profile, the AI tools in use, AI built into the business software you already pay for, personal and unmanaged devices (BYOD), MCP gateways, the assurance record, document-grounded AI answers, the agent inventory and agentic posture, agent permissions and your network logs.
You receive the Executive Risk Report, AI Acceptable Use Policy, Board Memo and AI Posture Summary, each dated and downloadable as PDF, Word, HTML, Markdown and plain text, with a Verification URL for each.
Catalog and registry refreshed monthly. Latest update: October 27, 2026
- ¹Non-human identities outnumber human identities ~100:1 — Astrix Security, via the CIS Controls v8.1 MCP Companion Guide (CIS / Astrix / Cequence), April 2026. Agents, service accounts, keys, and tokens now outnumber human identities by roughly 100 to 1 — and almost none are inventoried.
- ²80%+ of enterprise AI tools unmanaged — Zluri, State of AI in the Workplace 2025. Reports that IT and security teams have visibility and control over fewer than 20% of enterprise AI tools.
- ³59% of employees hide AI tool usage from IT — Cybernews 2025 AI Workplace Survey. Corroborated by KPMG’s April 2025 global study of 48,000 people across 47 countries (57%).