Insurers are asking on 2026 renewals now. What will you hand them? See what the law expects →
A dated AI posture history to price from.
MITRE and Mosaic Insurance’s new series, The New Economics of Cyber Risk, recommends a standing one-page brief and a posture update in the underwriting file, so an insured renews on “evidence rather than attestation.” SanctumShield produces the AI section of that brief: a dated AI Posture Summary, refreshed on the customer’s cadence, with every figure checkable at its verification URL.
What the Summary tells an underwriter
- Is there a current inventory of the AI tools and agents in use, and when was it last updated?
- Which agents can act on the organization’s behalf, and is each one’s permission approved and dated?
- What is the record of closing AI governance findings since the last summary?
- Which AI capabilities does the organization run that it did not build, including AI embedded in existing software?
- Is the AI use policy current, and when was it last reviewed by leadership?
Each answer comes from the insured’s own dated record. Where something is not yet recorded, the Summary says so. Over time the underwriter can see a track record, the series’ point that an insurer then “prices a track record instead of a form.”
Sources: MITRE and Mosaic Insurance, The New Economics of Cyber Risk, 2026 (four papers, public release PR 26-1675 to 26-1678), by James Tuplin and Jay Vinda (Mosaic Insurance), Dr. Sanith Wijesinghe and Chris Folk (MITRE). Quotations are from Paper 3, Buying Resilience.
Why underwrite AI risk blind?
By Lindsay Hiebert · Founder · CISSP
Renewal questionnaires now ask about AI governance — and a self-attested checkbox is all most applicants can offer. SanctumShield gives you an artifact instead: a dated, third-party-verifiable risk assessment and acceptable-use policy you can confirm in one click — no tenant access, no report contents exposed, metadata only. Require it before you bind; verify it again at every renewal.
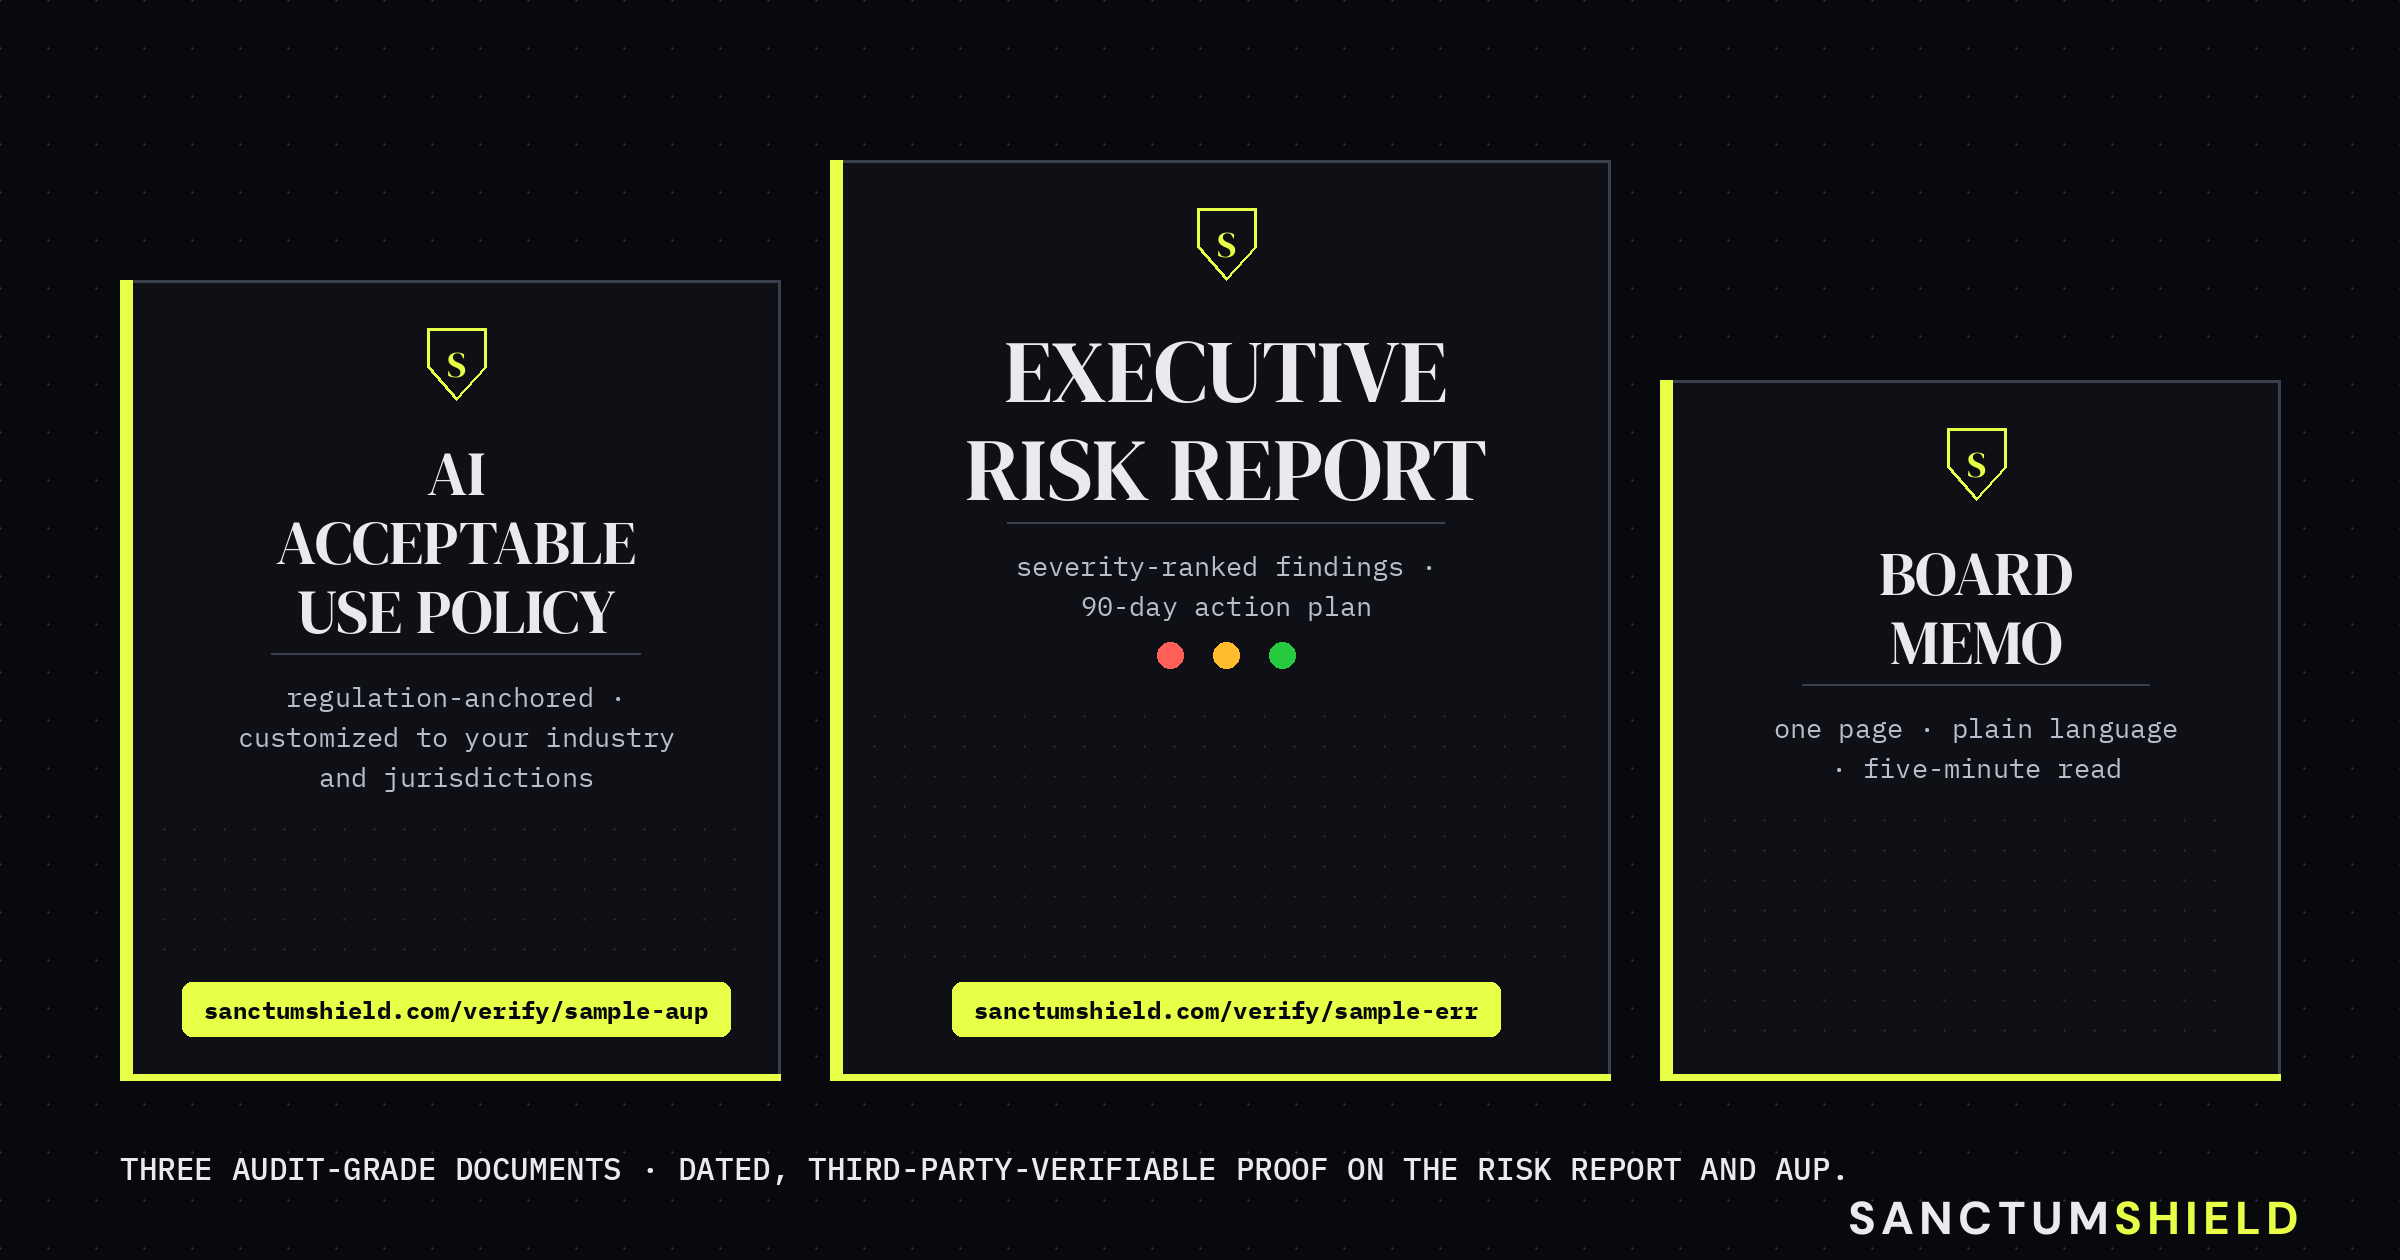
Four artifacts, underwriting-grade: the applicant’s AI Acceptable Use Policy, their Executive Risk Report, their Board Memo — and, on the Policy and the Risk Report, a Verification URL your desk can paste into a browser to confirm when SanctumShield produced the assessment. Evidence you verify, not a promise they make. The AI Posture Summary is the one-page view of all four.
An artifact dated last March tells you what was true last March. The cadence — re-run, re-dated, re-verifiable — is what turns governance from a one-time exhibit into a condition you can attach to eligibility.
Lower your cyber insurance bills and liabilities.
Lower the risk of the customers you insure.
The SanctumShield / cyber insurance channel is one of the rare strategies where the same artifact creates economic value on both sides of the table. The report that saves the applicant money is the same report that reduces loss exposure for the carrier. Here is the math for each side.
Lower your premium. Lower your retention.
Lower your exposure.
Cyber insurance premiums are priced off risk signals. Every carrier underwriting discount you earn — for MFA, for EDR, for phishing training, for an IR plan — exists because the control reduces loss frequency or severity. AI governance is the newest risk signal and the first one in a decade without a standardized measurement. A SanctumShield Executive Risk Report gives your broker a concrete artifact to walk into the renewal with and ask for:
- Premium reduction — a documented AI governance program with observed evidence is a rating factor your broker can raise at renewal
- Lower retention — self-insured retention (the deductible before the policy pays) often trades off against control maturity. Better controls, lower retention
- Narrower AI carve-outs — many 2025–2026 cyber policies are adding AI-risk exclusions. A carrier with an underwriting artifact has less reason to exclude
- Reduced personal liability — D&O exposure for “failure to supervise AI use” is rising. A regulation-anchored AUP and a risk assessment on file is the most defensible posture a CISO / GC can have
- Audit-ready evidence — the same report that reduces premium satisfies SOC 2, HIPAA, and enterprise procurement AI governance requirements. One artifact, five downstream wins
For a $40K–100K annual cyber premium, a 3–5% rating improvement is $1,200–$5,000 per year, every year the evidence stays current.
Lower loss ratio. Lower claims severity.
Lower the risk of the book you’re writing.
You are pricing AI risk right now without actuarial data. Every policy you write has an implicit AI exposure — shadow AI data exfiltration, prompt injection, AUP violations, regulatory penalties under the EU AI Act and state AI disclosure laws — and your loss reserves are sized against a risk you cannot yet observe. SanctumShield inverts that:
- Observed-network evidence — log-matched hits against a 118-domain AI endpoint registry. You see the AI the applicant actually uses
- Standardized risk score — a numeric output your actuaries can weight in existing rating models without a six-month data science project
- Regulation-anchored findings — each finding in the report mapped to a real clause in HIPAA, SOC 2, GDPR, or EU AI Act. Supports denial-of-claim defensibility and post-loss subrogation
- Loss ratio improvement — applicants who complete a SanctumShield assessment self-select into better governance posture. Lower loss frequency, lower severity, healthier book
- Differentiated product — first-mover carriers that reference SanctumShield in underwriting get a marketing edge in the mid-market: “our AI governance underwriting is quantitative and evidence-based”
- Regulatory defensibility — when a state insurance commissioner asks how your underwriting rationally distinguishes AI risk, a standardized third-party assessment is the answer they accept
A carrier that improves its loss ratio through better AI governance selection gains on every policy it writes, before the broker channel effects are counted.
Running SanctumShield produces the evidence and strengthens the governance program at the same time. The applicant who runs SanctumShield adopts a regulation-anchored AUP, a continuous registry of their AI tools, and a prioritized 90-day action plan as part of the assessment. The program gets stronger, the carrier sees a dated record of it, and the broker has a clear artifact to present.
One artifact. Three workflows.
Each one closes on its own merits.
Standardized AI risk input for underwriting.
The AI governance question already exists on most 2026 renewal forms as free text. SanctumShield converts that free text into a numeric risk score, prioritized, regulation-anchored findings, and a verification URL your underwriting team can paste to confirm that SanctumShield produced the report, and when. Reference it as a recommended input today; promote to required when your loss data supports it.
Precedent: external security ratings became common underwriting inputs as data-driven carriers adopted them. AI governance evidence can follow the same route.
Differentiate your book on AI governance.
Brokers are where the channel actually moves — you have the volume, the carrier relationships, and the renewal-cycle leverage. Recommend SanctumShield to covered clients as the AI governance artifact to attach to their renewal application. The verification URL means your carrier can confirm the record without any back-and-forth, and your client gets a board-ready deliverable as a side benefit.
MSSP / vCISO / consultant variants of this conversation are equally welcome — reach the founder to discuss broker-channel pricing.
Walk into the renewal with the artifact.
Run SanctumShield. Download the Executive Risk Report. Attach it to your renewal packet. Hand the verification URL to your broker; the broker forwards it to the underwriter. The underwriter pastes the URL, sees a clean attestation page, and now your AI governance section has a standardized, dated third-party signal.
Optional: tell us if you’d like a one-page brief sent to your carrier or broker. The opt-in form is at the bottom of this page — courtesy notification, not a campaign.
Where SanctumShield fits for Colorado-regulated carriers — and where it does not.
The Colorado AI Act ( Senate Bill 26-189, which repealed and replaced SB 24-205, effective January 1, 2027) expressly safe-harbors insurers and entities subject to Colorado § 10-3-1104.9 (the existing insurance-AI rule) from Part 17 of CRS Title 6, Article 1 — in the practice of insurance. That means a Colorado-domiciled carrier’s actual underwriting, pricing, claims, and rating activities are governed by § 10-3-1104.9 and are deemed compliant with the new Part 17 obligations for those domains.
SanctumShield’s value to Colorado-regulated carriers is therefore not “we make you compliant with the AI Act for underwriting and pricing” — that domain is already addressed by the insurance rule. The live SanctumShield hooks for Colorado-domiciled insurers are the carrier’s non-insurance ADMT exposure — specifically:
- Employment-related ADMT use — AI tools used in candidate screening, performance management, or compensation decisions affecting Colorado-resident employees fall under SB 26-189’s employment-covered-domain obligations, regardless of the carrier’s insurance safe harbor
- Non-insurance consequential decisions — marketing AI, customer-service AI, vendor- onboarding AI, internal-decisioning AI outside the practice of insurance remain in scope for SB 26-189
- Documented scope-exemption AUP — generative-AI tools (ChatGPT, Claude, Copilot, etc.) that the carrier uses internally and that are governed by an AUP prohibiting consequential-decision use can rely on the SB 26-189 two-condition exemption. SanctumShield’s Section 16 codifies that exemption in audit-ready language
In short: SanctumShield’s value to the carrier’s own internal AI use is real (non-insurance domains). SanctumShield’s value to the carrier’s underwriting workflow — using the Executive Risk Report and verification URL as inputs to score the applicant’s posture — remains the bilateral value prop described above. The two value props are distinct and the insurer safe harbor applies only to the first.
This disclosure addresses a clarification raised in external review of the SanctumShield carrier positioning following the May 14, 2026 signing of SB 26-189. See the glossary entries for Covered ADMT, Consequential Decision, and ADMT Scope Exemption for the full statutory framing.
Each tool underwriting references today
measures its own risk surface well.
When a cyber underwriter reaches for a third-party signal, they reach for a vulnerability scanner, an external attack-surface rating, or a compliance-automation dashboard. SanctumShield adds the AI layer beside them: the AI tools and agents an organization actually uses, observed in its own network logs, and a dated, regulation-anchored record of how it governs them.
CVEs on operating systems, network services, and web applications. Patch reporting for Microsoft servers. Compliance against CIS benchmarks. Strong at what it measures.
An inventory of the AI tools in use, matched against observed AI endpoint traffic, with each tool's data-use terms, and an AI Acceptable Use Policy mapped to the EU AI Act and NIST AI RMF.
Unpatched hosts, exposed services, misconfigurations, known exploitable vulnerabilities on infrastructure you own. Strong at what it measures.
The AI services employees reach over everyday HTTPS from browsers and SaaS, matched against the AI endpoint registry, with a governance record and a named owner for each.
Externally observable posture: DNS hygiene, certificate quality, leaked credentials, open ports, botnet activity, patching cadence inferred from HTTP headers. Valuable for procurement triage and insurance baseline.
The inside view: the AI tools and agents the organization's people actually use, with named owners, so the external rating and an internal AI record sit side by side in the submission.
SOC 2 and ISO 27001 control inventories, evidence collection, audit preparation workflows. Invaluable for the audits they accelerate.
An observation-based AI risk assessment: findings from the organization's own network logs, each anchored to a specific regulatory clause with an owner, plus the AI Acceptable Use Policy and Board Memo, each with a dated verification record.
SanctumShield is a formal, rigorous, recent, regulation-anchored AI risk assessment, built for AI from the start.
Formal assessment. The Executive Risk Report is structured: score, headline, prioritized findings, business impact, prioritized action plan with named owners and effort levels. Every finding cites a real clause — HIPAA §164.502(e), SOC 2 CC6.1, EU AI Act Article 5, NIST AI RMF GOVERN-1.4 — verifiable against source law. A defensible assessment. Each action in the Executive Risk Report names the finding it closes, so an underwriter can trace every control to the risk it answers.
Rigorous methodology. Inputs are the company profile, the AI tools the organization declares, and its own observed firewall, proxy and DNS traffic, assessed against a catalog of 130 AI tools and built-in AI features, and a registry of 118 known AI endpoints matched against your network logs. Observation over attestation.
Recency. The registry, the regulatory citations, the tools catalog, and the policy prompts are refreshed monthly. See the latest changelog. SanctumShield refreshes against the AI landscape every month.
Rescans are trivial. Because the methodology is pure-function on inputs, re-running the assessment with updated traffic, an updated tools list, or the latest monthly registry refresh takes minutes. No deployment cycle. No reassessment project. No change management.
Targeted. SanctumShield does one thing: the AI risk record. It works alongside your SIEM, EDR, DLP, GRC platform, compliance automation and vulnerability scanner, and adds the specific artifact your board and your insurer are asking for.
Four reasons AI governance evidence matters to cyber underwriting.
AI use creates loss scenarios carriers are learning to price: data exposure through AI tools, prompt injection, and policy violations that carry regulatory exposure. Actuarial data is still thin, so a standardized, dated input helps underwriters see what an applicant actually runs.
Cyber renewal questionnaires increasingly include questions about AI governance, often as free-text fields about AUP existence, AI tool inventory and training policy. A standardized report with a risk score and regulation-anchored findings turns those answers into a consistent input. SanctumShield produces exactly that artifact.
MFA, EDR, backup and recovery, phishing training and incident response plans became common cyber underwriting expectations as carriers learned what reduces loss. AI governance evidence can follow the same path, and a standardized tool built for the mid-market that produces a clean, dated PDF makes it easy for carriers to reference.
The customer gets an answer to the board-pressure question. The carrier gets a standardized risk input they can price against. The broker gets a clear PDF they can attach to the application. Each side gets something it needs.
Every report comes with
a verification URL — the underwriter can confirm the record in one click.
Every paid SanctumShield report — both the AI Acceptable Use Policy and the Executive Risk Report — carries a unique verification URL printed in the document footer. Your underwriter pastes that URL into a browser and immediately sees a confirmation page showing when the report was generated, by whom, with which AI model, and against which endpoint registry version. The contents of the report are never exposed; the record shows only that SanctumShield generated a document with that ID for that organization on that date. Records are kept for six years so the same URL works across multiple renewal cycles.
The AI Posture Summary is the one-page view of all four, with each source’s verification URL printed on it.
A unique verification URL is printed in the document footer when you download the .docx — for example, sanctumshield.com/verify/abc123xyz.
Attach the .docx (or PDF print of it) to your renewal application packet, your SOC 2 evidence folder, or your board memo — wherever it needs to go.
They open a browser, paste the verification URL, and see a clean attestation page showing the date, AI model, and registry version SanctumShield used to generate your report.
The underwriter can confirm that SanctumShield issued the report on the date shown, without seeing its contents and without access to your tenant.
Every SanctumShield artifact is issued from a queryable record. An underwriter pastes the URL and confirms the record in one step. The record shows what SanctumShield issued and when, without exposing the document’s contents, and the same URL keeps working across renewal cycles for six years.
- → That SanctumShield issued the document with that ID
- → The organization it was issued for and the date it was generated
- → The AI model and the endpoint registry version used
- → Whether the organization later attested an edited version, with a link between the original and the attested record
Want a one-page brief sent to your carrier or broker?
If you’d like SanctumShield to send a one-page briefing to your cyber insurance carrier or your broker — explaining what the artifact is and how verification works — drop your details below. This is opt-in only. There is no public counter, no “pledge wall,” no aggregate marketing. The form below routes directly to the founder and the outreach is tailored, not bulk. CISOs at insured organizations and brokers serving covered clients are both welcome.
If you underwrite cyber at mid-market scale,
we should talk this week.
What we’re offering
- An underwriter-format Executive Risk Report with a numeric risk score, regulation-anchored findings, and a 90-day action plan, produced from a guided review at the level you choose (Light, Standard or Complete)
- Coverage of seven frameworks (HIPAA, GDPR, CCPA, SOC 2, NIST AI RMF, EU AI Act, ISO 27001) with real clause citations
- Observed-network evidence via applicant-provided firewall / proxy / DNS logs, matched against a continuously maintained 118-domain AI endpoint registry
- A verification URL so your underwriting team can confirm that SanctumShield generated the report on the date shown
- Per-assessment pricing, bulk licence pricing, or white-label options — we’ll structure whatever fits your underwriting workflow
- Direct technical access to the founder, a CISSP with more than 20 years at Cisco and Intel
- Departmental and line-of-business assessment scoping — for larger insureds where AI risk varies materially across business units (clinical vs. corporate, retail bank vs. wealth management, federal vs. commercial), SanctumShield can produce unit-level reports that give underwriters granular visibility into where the actual AI exposure sits
What we’re asking
- A 20-minute call with the underwriter responsible for your AI governance questions on the cyber renewal form
- An honest evaluation of whether the Executive Risk Report would be useful as an underwriting input, a pricing signal, or a post-bind advisory artifact
- A no-commitment pilot on 5–10 applicants at renewal — we will run the reports on your request, you read them, you decide
- If the pilot works, a conversation about making the report a formal input to the AI governance section of your underwriting workflow
External security ratings became common cyber underwriting inputs as data-driven carriers adopted them. SanctumShield gives AI governance the same kind of consistent, dated input, built for the underwriting channel.
For coverage disputes, subrogation actions, and post-incident standard-of-care assessments where AI governance evidence is contested, SanctumShield’s founder Lindsay Hiebert (CISSP) accepts a limited number of expert witness and investigative consulting engagements. See Expert Witness & Investigative Consulting.
The board meeting is coming. The renewal is coming.
The artifact is ready when you are.
What SanctumShield covers
For underwriters and brokers: one consistent, dated record per applicant, renewed on the applicant's own cadence.
130 AI tools and built-in AI features (82 tools, 48 built-in features) and 118 known AI endpoints matched against your network logs.
The assessment covers your company profile, the AI tools in use, AI built into the business software you already pay for, personal and unmanaged devices (BYOD), MCP gateways, the assurance record, document-grounded AI answers, the agent inventory and agentic posture, agent permissions and your network logs.
You receive the Executive Risk Report, AI Acceptable Use Policy, Board Memo and AI Posture Summary, each dated and downloadable as PDF, Word, HTML, Markdown and plain text, with a Verification URL for each.
Catalog and registry refreshed monthly. Latest update: October 27, 2026
Carriers themselves sit under model risk management expectations in the US (SR 26-2, 2026) and Canada (OSFI E-23, 2027); an insured’s AI system register and Executive Risk Report answer the same inventory, ownership and monitoring questions for the AI those guidelines do not name. Model Risk Management (MRM)